Cybersecurity Services Engineered for Trust, Resilience & Digital Continuity
Security is no longer a technical consideration that sits behind the business. It is part of the experience a business creates, the systems it operates and the trust it earns.
As applications become more connected and organizations increasingly depend on cloud infrastructure, APIs, data platforms and digital workflows, the security landscape becomes more complex. A single overlooked vulnerability can extend far beyond a technical issue—affecting operations, customer confidence, sensitive information and business continuity.
Digital Raiz provides cybersecurity services and digital security solutions designed to help organizations understand their exposure, strengthen their technology environments and build greater resilience against evolving cyber risks.
Our approach looks beyond isolated vulnerabilities. We consider how applications, infrastructure, data, identities and integrations interact to create a broader security environment.
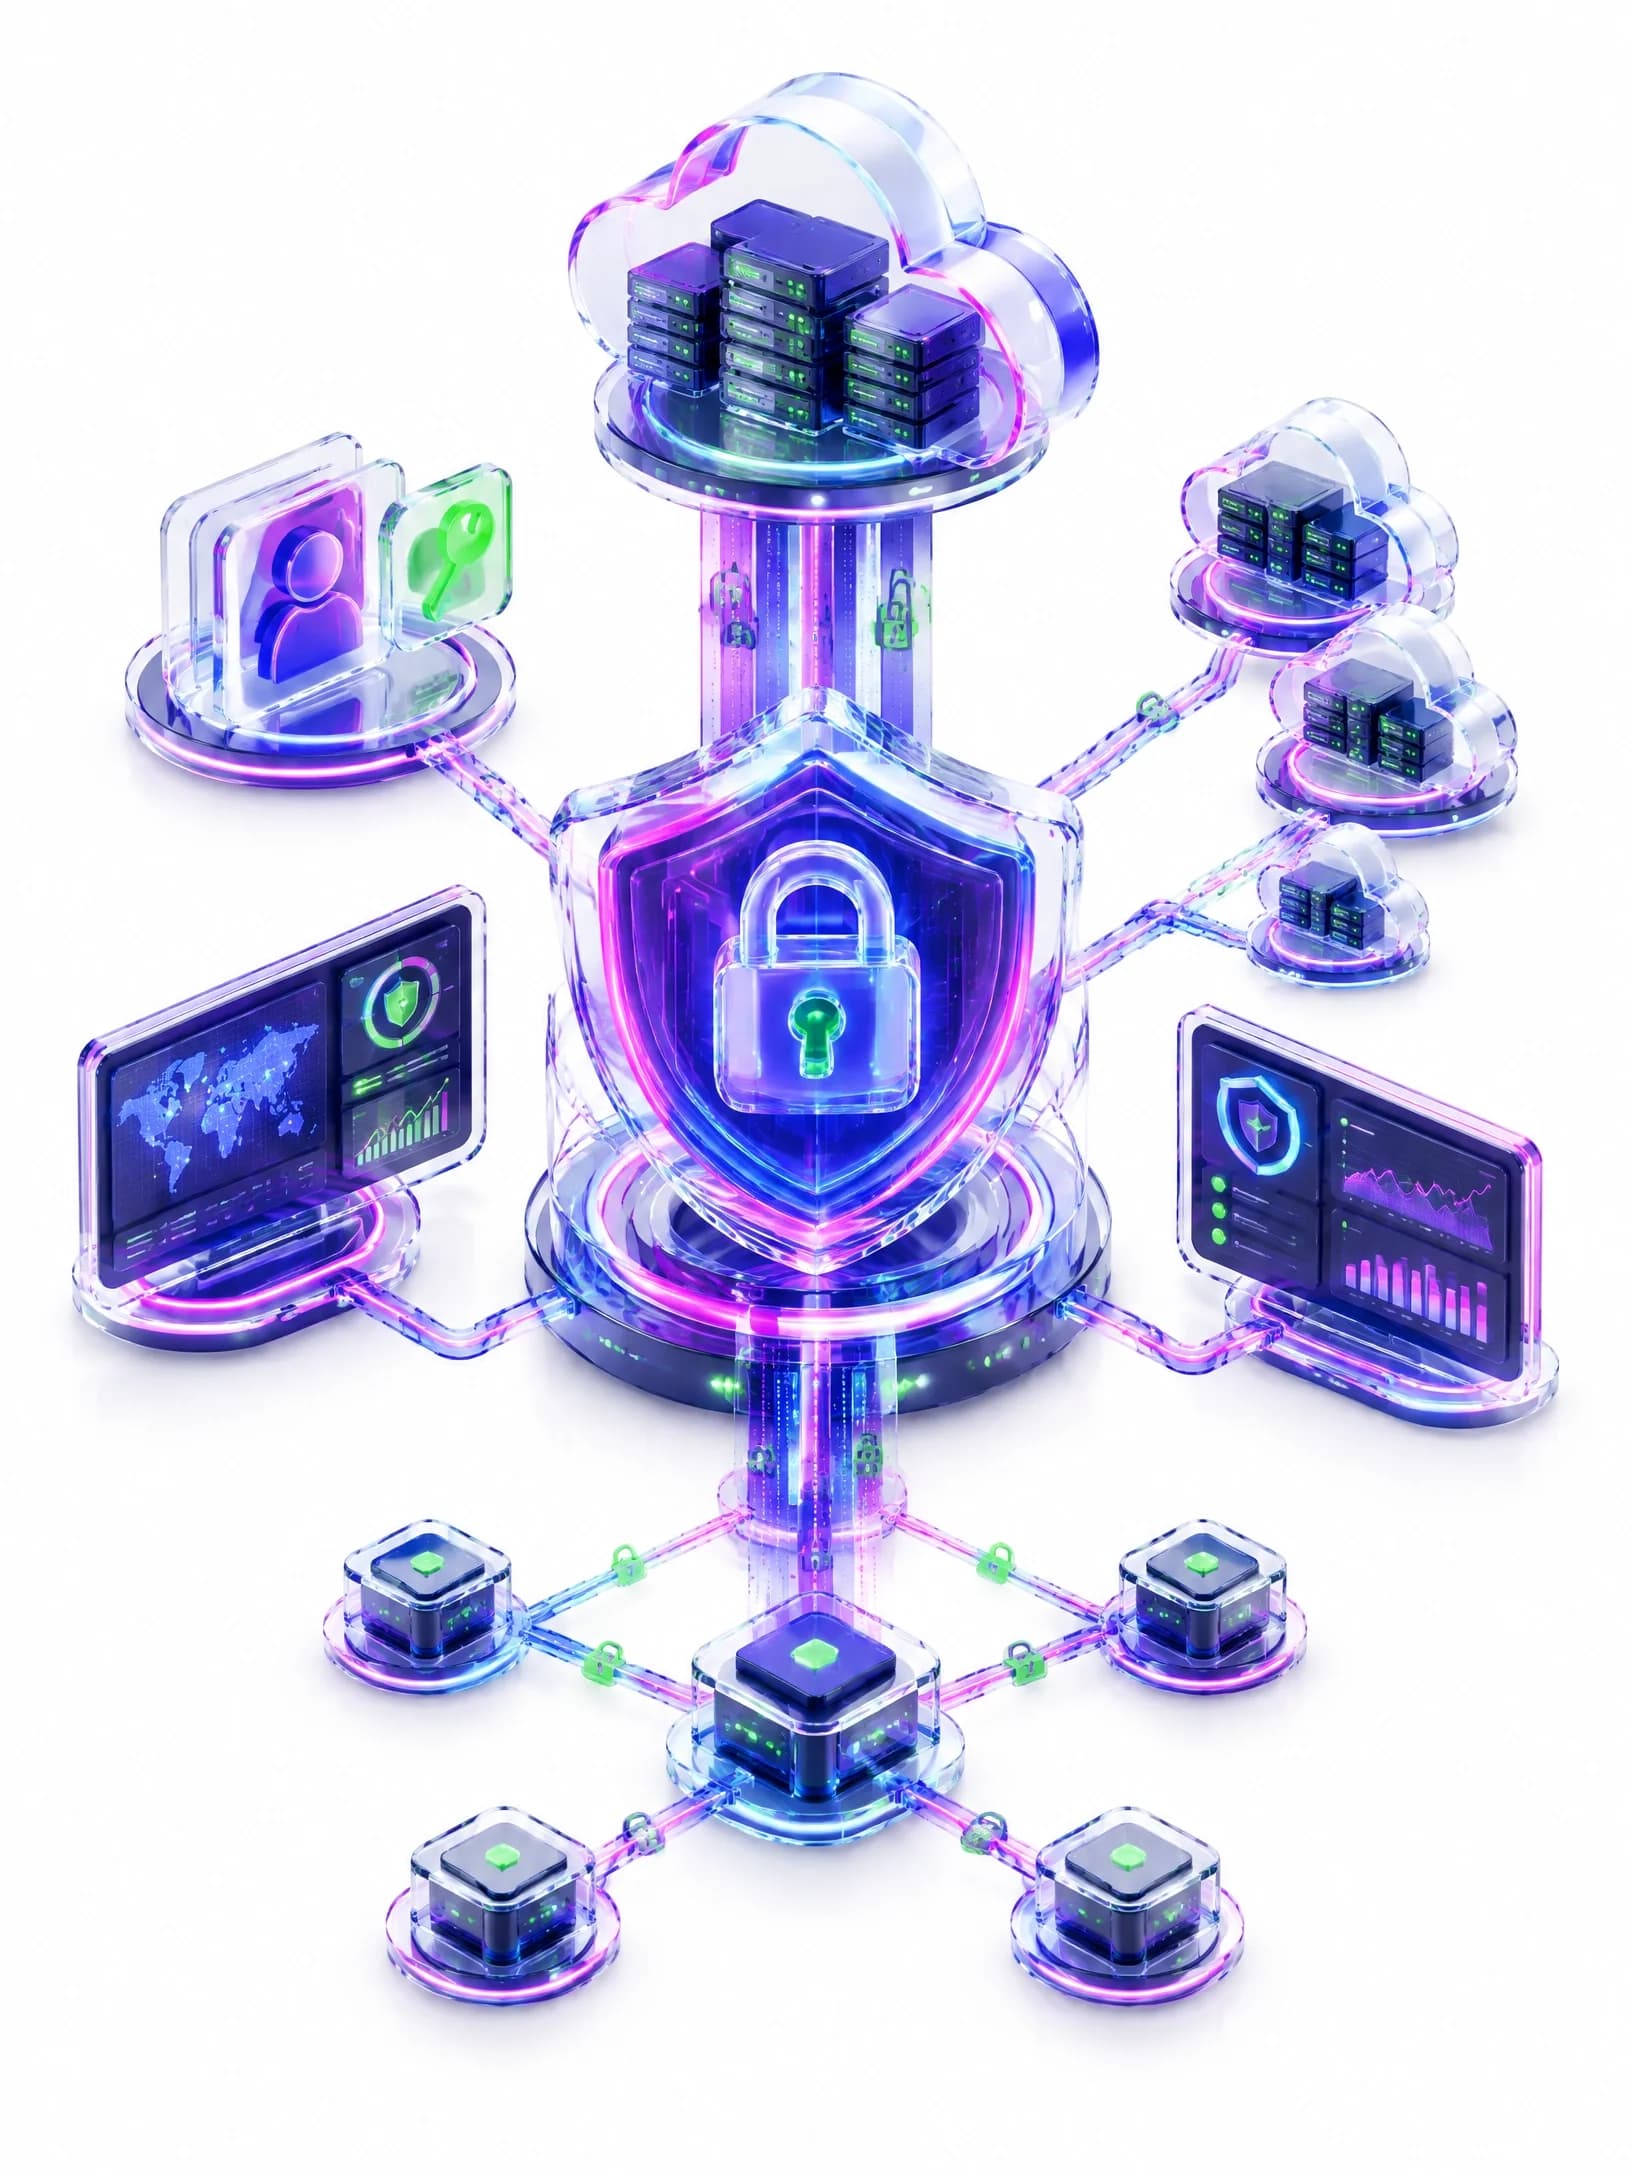
Turning the Attack Surface Into a Strategic Security Perspective
Every digital environment has an attack surface. The challenge is knowing where exposure exists before someone else discovers it.
Digital Raiz helps organizations examine their technology landscape through structured cybersecurity assessment, vulnerability assessment and security testing. We evaluate applications, systems and digital environments to identify weaknesses that could affect confidentiality, integrity, availability or user trust.
Our application security services cover modern web and mobile applications, helping identify security concerns across application behaviour, authentication, authorization, data handling, APIs and connected services. We also consider the relationships between applications and the infrastructure supporting them, because security rarely ends at the application layer.
Our 9 Core Cybersecurity Capabilities
Complete CoverageWeb Application Security
Comprehensive protection for web platforms, addressing application behavior, authentication, authorization, APIs, and connected microservices.
Mobile Application Security
Rigorous security evaluations across iOS & Android apps, securing local data storage, auth tokens, third-party SDKs, and mobile API communication.
Cloud Security
Essential protection for workloads, containers, and data platforms across cloud environments to maintain control, visibility, and operational resilience.
Network Security
Safeguarding corporate perimeters, internal segments, VPN gateways, and micro-segmentation architectures against unauthorized access and traffic spoofing.
Vulnerability Assessment
Structured examination of technology landscapes, scanning applications, databases, and networks to discover security weaknesses before exploitation.
Security Testing
Systematic automated and manual testing evaluating confidentiality, integrity, availability, and user trust across all digital environments.
Information Security
Protecting sensitive enterprise data, customer PII, internal intellectual property, and critical databases from unauthorized access or exfiltration.
Risk Assessment
Prioritizing remediation efforts based on exposure impact, business continuity requirements, and technology realities to make informed decisions.
Application Security
Embedding security practices earlier in the development lifecycle to ensure applications are built securely from ground level to production deployment.
"The objective is not to create fear around technology. It is to create visibility around risk."
When organizations understand where weaknesses exist, they can prioritize remediation, make better technology decisions and build security into the products and systems they depend on.
Designing Digital Environments Where Security Is Part of the Architecture
Strong cybersecurity is not defined by a single tool, assessment or security layer. It is created through a continuous understanding of technology, people, processes and potential threats.
Technology Lifecycle Protection
Digital Raiz brings a security-first perspective to digital environments, helping businesses consider protection throughout the technology lifecycle—from development and deployment to infrastructure, integration and ongoing operation.
Tailored Cybersecurity Consulting
Our cybersecurity consulting services are designed around the realities of each organization rather than a one-size-fits-all checklist. We consider the technology landscape, business priorities and areas of exposure to establish practical security priorities.
Early Product Security & Testing
For businesses building digital products, security can be incorporated earlier through secure development practices and application-focused testing. For organizations operating established environments, security assessments can help uncover areas that require attention as systems, integrations and threats evolve.
Resilient Cloud Security
Cloud adoption introduces another dimension to this landscape. As workloads, applications and sensitive information move across cloud environments, cloud security becomes an essential part of maintaining control, visibility and resilience.
"The goal is a digital environment that can continue operating with confidence—even as technology changes and the threat landscape evolves."
"Digital Raiz approaches cybersecurity as an architectural discipline, helping businesses protect what they build, understand what they expose and create digital environments founded on resilience, trust and long-term continuity."
6 Core Cybersecurity Command Pillars
Select a cyber defense module below to inspect its zero-trust capabilities, tools, and deliverables.
Zero-Trust Architecture & IAM Governance
Enforce strict multi-factor authentication (MFA), role-based access control (RBAC), and least-privilege credentials across all cloud apps and microservices.
Our 6-Stage Cybersecurity & Pentesting Process
A battle-tested 6-phase security remediation lifecycle designed to neutralize threats before production deployment.
Why Global Enterprises Trust Digital Raiz for Cybersecurity & VAPT
Deploy pre-vetted OSCP and CEH certified ethical hackers ready to audit and secure your infrastructure within 48 hours.
Hire Certified Ethical Hackers & DevSecOps Engineers
Augment your internal security squad with certified OSCP, CEH, and CISSP ethical hackers ready to conduct deep VAPT pentesting and zero-trust hardening.
8 Core Cybersecurity Assurance Pillars
Zero-Trust SLA100% Zero-Trust Audit
Identity & secrets management hardening
48-Hr Squad Match
Instant pre-vetted OSCP hacker onboarding
OWASP Top 10 Remediation
Complete vulnerability patching SLA
CI/CD DevSecOps
Automated SAST & container security gates
24/7 SIEM & SOC Alerts
Real-time log telemetry & anomaly alerts
ISO 27001 & SOC2 Audit
Compliance automation & PII masking
API Vulnerability Scans
REST & GraphQL pentesting proofs
15-Min Incident SLA
Rapid SOC emergency response team
Ready to Secure Your Enterprise Infrastructure with Digital Raiz?
Zero-Trust Architecture • VAPT Pentesting • Web & Mobile App Security • ISO 27001 Compliance